What is Threat Detection and Response, and Why Does It Matter for Network Defense?
The goal of threat detection and response is basically just one thing: identify potential threats early and prevent them from escalating into an actual incident. Therefore, a threat detection and response strategy is focused on the identification, investigation, and containment of cybersecurity threats as they relate to an organization’s networks, endpoints, and cloud infrastructures.
A modern threat detection platform provides organizations with ongoing visibility regarding their network threat detection efforts. The increased visibility enables security practitioners to more quickly identify suspicious activity, investigate it with a higher level of confidence, and react before an attacker has an opportunity to build any momentum. The best threat detection and response platforms will utilize the power of analytics, automation, and contextualized information in combination to provide the highest possible level of security for the networks they protect while also minimizing the negative impact on the organization from the associated attacks.
Introduction
After almost 25 years in cybersecurity, NetWitness remains influential in how organizations tackle solutions for threat detection and response. Initially a U.S. government research program aimed at network threat detection, it has transformed into a reliable platform employed by companies to safeguard intricate environments.
Since the start, NetWitness was designed with a straightforward concept: security teams require complete visibility, relevant context, and the capability to respond quickly. That same principle continues to characterize NetWitness today, establishing it as a reputable threat detection platform for organizations encountering more advanced threats.
How NetWitness Evolved Over the Years
NetWitness has evolved alongside the changing needs of security teams. What began as a research initiative focused on analyzing large volumes of network data developed into a broader platform for threat detection, investigation, and response.
The evolution can be traced through several key stages:
- 1997: NetWitness began as a U.S. intelligence research initiative designed to help analysts understand large volumes of captured network data.
- 2006: NetWitness entered the commercial market as a packaged network analysis solution.
- 2011: RSA acquired NetWitness, bringing network packet analysis together with SIEM capabilities and expanding its enterprise security use cases.
- Later evolution: The platform expanded with capabilities including behavioral analytics, UEBA, SOAR, full-packet capture, and deeper investigation workflows.
- Today: NetWitness provides unified visibility and analytics across networks, endpoints, and log data to support modern threat detection and response.
This evolution also reflects a broader shift in cybersecurity. Security teams have moved from analyzing isolated network events to correlating data, investigating threats in context, and automating appropriate response actions. Threat detection automation and security investigation automation now play a growing role in helping analysts work through the volume and complexity of modern security data.
The underlying principle, however, has remained consistent: give security teams the visibility and context they need to understand what is happening and respond with confidence.
From Network Analysis to Modern Threat Detection
The shift from network analysis to modern threat detection has been driven by one fundamental change: security teams now need to understand not only what happened on the network, but also whether an activity represents a threat, how it relates to other events, and what action should follow.
Early NetWitness capabilities focused on real-time packet capture, network analysis, and metadata-driven investigation. As enterprise environments became more complex, those capabilities expanded to support broader security operations.
Modern threat detection brings together multiple layers of visibility and analysis. Network traffic, endpoint activity, logs, behavioral analytics, threat intelligence, and response workflows can work together to give analysts a more complete view of suspicious activity.
This is where security automation tools for better threat detection become valuable. Automation can help correlate events, enrich findings, prioritize suspicious activity, and initiate response workflows while analysts focus on investigation and decision-making.
NetWitness reflects this progression from network analysis to a unified approach to threat detection, investigation, and response. Its platform combines network visibility, endpoint and log data, analytics, and automation to help security teams move from identifying suspicious activity to understanding and responding to it.
|
Then |
Now |
|
Network traffic was the primary source of investigation data. |
Security teams’ correlate network, endpoint, log, and behavioral data. |
|
Analysts focused heavily on packet capture and network analysis. |
Analysts investigate activity across multiple security data sources. |
|
Investigation often depends on manually examining data. |
Analytics and automation help accelerate detection, investigation, and response. |
|
Detection focused primarily on identifying suspicious network activity. |
Modern threat detection connects detection with investigation and response. |
|
Security data could exist in separate systems. |
Unified platforms can bring security data and investigation workflows together. |
|
Analysts needed to manually connect individual events. |
Correlation and contextual analytics help build a clearer picture of an attack. |
|
Response followed detection as a separate step. |
Detection and response can be connected through automated and guided workflows. |
The evolution reflects NetWitness’s progression from network analysis and packet-based investigation toward a broader threat detection and response platform.
Why NetWitness Stands Out as a Threat Detection and Response Platform
NetWitness delivers the core capabilities security teams expect from the best threat detection and response solutions: visibility, context, without unnecessary complexity.
- Deep visibility across networks, endpoints, and logs to support network threat detection.
- Event correlation with rich context to accelerate investigations and cyber threat hunting.
- Integrated UEBA, SOAR, and analytics within a single threat detection platform.
- Scalable architecture designed for on‑prem and hybrid network defence environments .
- Proven support for organizations using managed threat detection and response solutions.
This focus allows NetWitness to help teams move beyond alert overload and toward practical, decision‑ready security outcomes.
A Legacy Built on Real-World Threat Detection
NetWitness’s past continues to shape its strategy toward contemporary cyber security challenges and remedies. After gaining independence from RSA and Dell EMC, the company acquired the freedom to enhance innovation, allocate resources for research, and broaden its threat detection and response offerings.
These foundational elements were vital in developing current threat detection and response systems, particularly in settings where precision, transparency, and rapidity are crucial for efficient network protection.
From Network Analysis to Enterprise Cyber Defence
NetWitness began in 1997 as a research initiative under CTX Corporation, where it was developed to help analysts interpret large volumes of network data. The technology proved valuable across multiple investigative use cases and was later refined under ManTech International to support federal law enforcement operations.
By 2006, NetWitness entered the commercial market as a packaged software solution. Many early adopters continue to rely on the platform today, a testament to its durability and relevance in evolving cybersecurity threats.
Early innovations included:
- Real‑time packet capture and analysis
- Metadata-driven investigation for faster triage
- Support for high‑security and intelligence‑driven environments
- The groundwork for scalable threat detection and response solutions
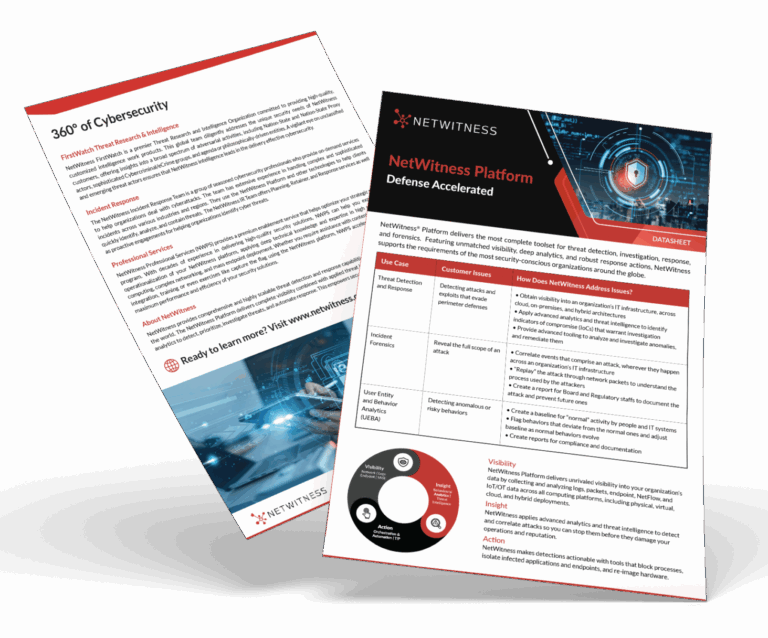
360° Cybersecurity with NetWitness Platform
– Unrivaled visibility into your organization’s data
– Advanced behavioral analytics and threat intelligence
– Threat detections and response actionable with the most complete toolset
SIEM Integration and the Expansion of Network Defense
The acquisition of NetWitness by RSA in 2011 marked a pivotal moment. By integrating SIEM log data with packet analysis, NetWitness expanded its enterprise reach and strengthened its network threat detection capabilities.
This convergence enabled behavior‑driven threat detection and response, moving beyond traditional log analysis and supporting more effective cyber threat hunting. The result was stronger network defense and faster, more confident response decisions.
The NetWitness Platform: Unified Threat Detection and Response
With the addition of UEBA and SOAR capabilities, NetWitness evolved into a comprehensive threat detection and response platform. This unified approach supports both managed and in‑house teams dealing with modern cyber security threats and solutions.
Key capabilities include:
- Behavioral analytics for anomaly detection
- Automated and guided response workflows
- Full‑packet capture and deep inspection
- Flexible support for diverse security operations models
NetWitness 12.3 and the Modern Security Landscape
NetWitness 12.3 strengthens the platform’s role in enterprise network threat detection, particularly across hybrid, cloud, and remote environments. The release improves asset visibility, prioritization, and investigation using advanced analytics.
This evolution reinforces NetWitness as a centralized threat detection platform designed to help organizations respond effectively to today’s cybersecurity threats.
A New Era for Threat Detection and Response
As an independent company, NetWitness continues to invest in its people, technology, and partnerships. Its focus remains steady: delivering practical, intelligence‑driven threat detection and response solutions that help organizations defend against real‑world attacks.
Rather than positioning itself as just another security vendor, NetWitness operates as a long‑term partner, working closely with customers to strengthen network defense, improve cyber threat hunting, and reduce risk across the enterprise.
Frequently Asked Questions
1. How does threat detection and response work?
It integrates ongoing monitoring, analytics, and automation to detect, analyze, and manage cybersecurity threats instantly.
2. How do organizations respond to threats using threat detection and response solutions?
Security teams utilize a threat detection system to examine alerts, conduct cyber threat hunting, and automate response measures.
3. Why is threat detection and response important for network defense?
It shortens the time attackers spend, minimizes operational effects, and enhances decision-making amid ongoing incidents
4. What are managed threat detection and response services?
These services use expert monitoring and cyber threat hunting. They also include a threat detection and response platform for ongoing protection.
5. How does NetWitness support modern threat detection and response?
NetWitness supports modern threat detection and response by combining network, endpoint, and log visibility with analytics, threat intelligence, behavioral analysis, investigation, and response capabilities. This helps security teams detect suspicious activity, investigate it in context, and take action through guided or automated workflows.
The platform also supports threat detection automation and security investigation automation, helping analysts correlate relevant data, prioritize activity, and accelerate investigation and response. Full-packet capture and deep inspection provide additional context for validating alerts and reconstructing activity when deeper investigation is required.
Evaluate unified security platforms with confidence using a practical guide to essential capabilities.