Every system in your organization speaks their mind through logs. Your web servers record every request. Your firewalls monitor every connection attempt. Your applications document every transaction or error. But these logs remain scattered throughout the network. These fragmented logs do not show the whole picture.
That is where log aggregation comes in. Let’s look at what it means and what are the benefits of log aggregation in cybersecurity space.
What is meant by Log Aggregation?
Log aggregation is the process of collecting log data from multiple sources across your IT infrastructure. It consolidates the logs and stores them in a centralized location where it can be analyzed and searched effectively.
Log aggregation tools helps security teams to monitor activity across the organization in real-time, troubleshoot issues, investigate incidents, and meet compliance requirements.
What is the Difference Between Log Collection and Log Aggregation?
Log aggregation is often confused with log collection. But log aggregation goes several steps beyond log collection.
Log collection is a simple act of gathering logs from various systems and moving them somewhere else, if required.
Log aggregation on the other hand is collecting logs from various systems, parsing them into a uniform format, adding contextual information, correlating it to specific events, and finally organizing them in a fashion that facilitates easy searching and analysis.
For example: Log collection is installing security cameras on each floor in the office. Each camera records footage on its own system. So, while the footage exists, it is fragmented and to understand the entire sequence of an event, one must go through each floor and footage files separately and connect the dots.
Log aggregation is when all the recordings are put together and accessible in a central control room. The security team can view, search, and correlate all the footage from every floor from one place.
How Does Log Aggregation Work?
Log aggregation is more than forwarding log files to a central server. The process typically involves several stages, from generating the data to making it searchable for the teams that need it.
1. Log generation
Applications, operating systems, servers, databases, network devices, cloud platforms, and security products continuously generate logs as events occur. These records can include authentication attempts, system changes, application errors, network connections, and other activity.
2. Log collection
A log aggregation solution collects these records from their respective sources. Depending on the environment, collection may use agents, Syslog, APIs, connectors, or other supported protocols.
The goal is to bring data from different parts of the infrastructure into the aggregation pipeline without creating gaps in coverage.
3. Log ingestion and parsing
Once collected, logs are ingested into the platform and parsed so that useful fields can be identified. A raw event might contain a timestamp, hostname, username, IP address, event type, or status code, but those details may appear in different formats across different sources.
Parsing makes the information easier to work with and search.
4. Normalization and enrichment
Logs from different technologies rarely follow the same structure. Normalization helps bring similar information into a consistent format.
Additional context can also be associated with events where supported, helping analysts understand what happened, where it happened, and which users, systems, or services were involved.
5. Centralized storage and indexing
The processed logs are stored in a central repository and indexed for faster retrieval. Retention policies can determine how long different types of logs remain available based on operational, security, or compliance requirements.
6. Search and analysis
With the data in one place, teams can search across multiple log sources instead of checking individual systems one at a time. This can help with troubleshooting, incident investigation, threat hunting, compliance reviews, and operational monitoring.
The important point is that aggregation creates the foundation for the analysis that happens later. NetWitness describes a similar pipeline across its log-monitoring and log-management guidance, including ingestion, aggregation, parsing, indexing, storage, and analysis
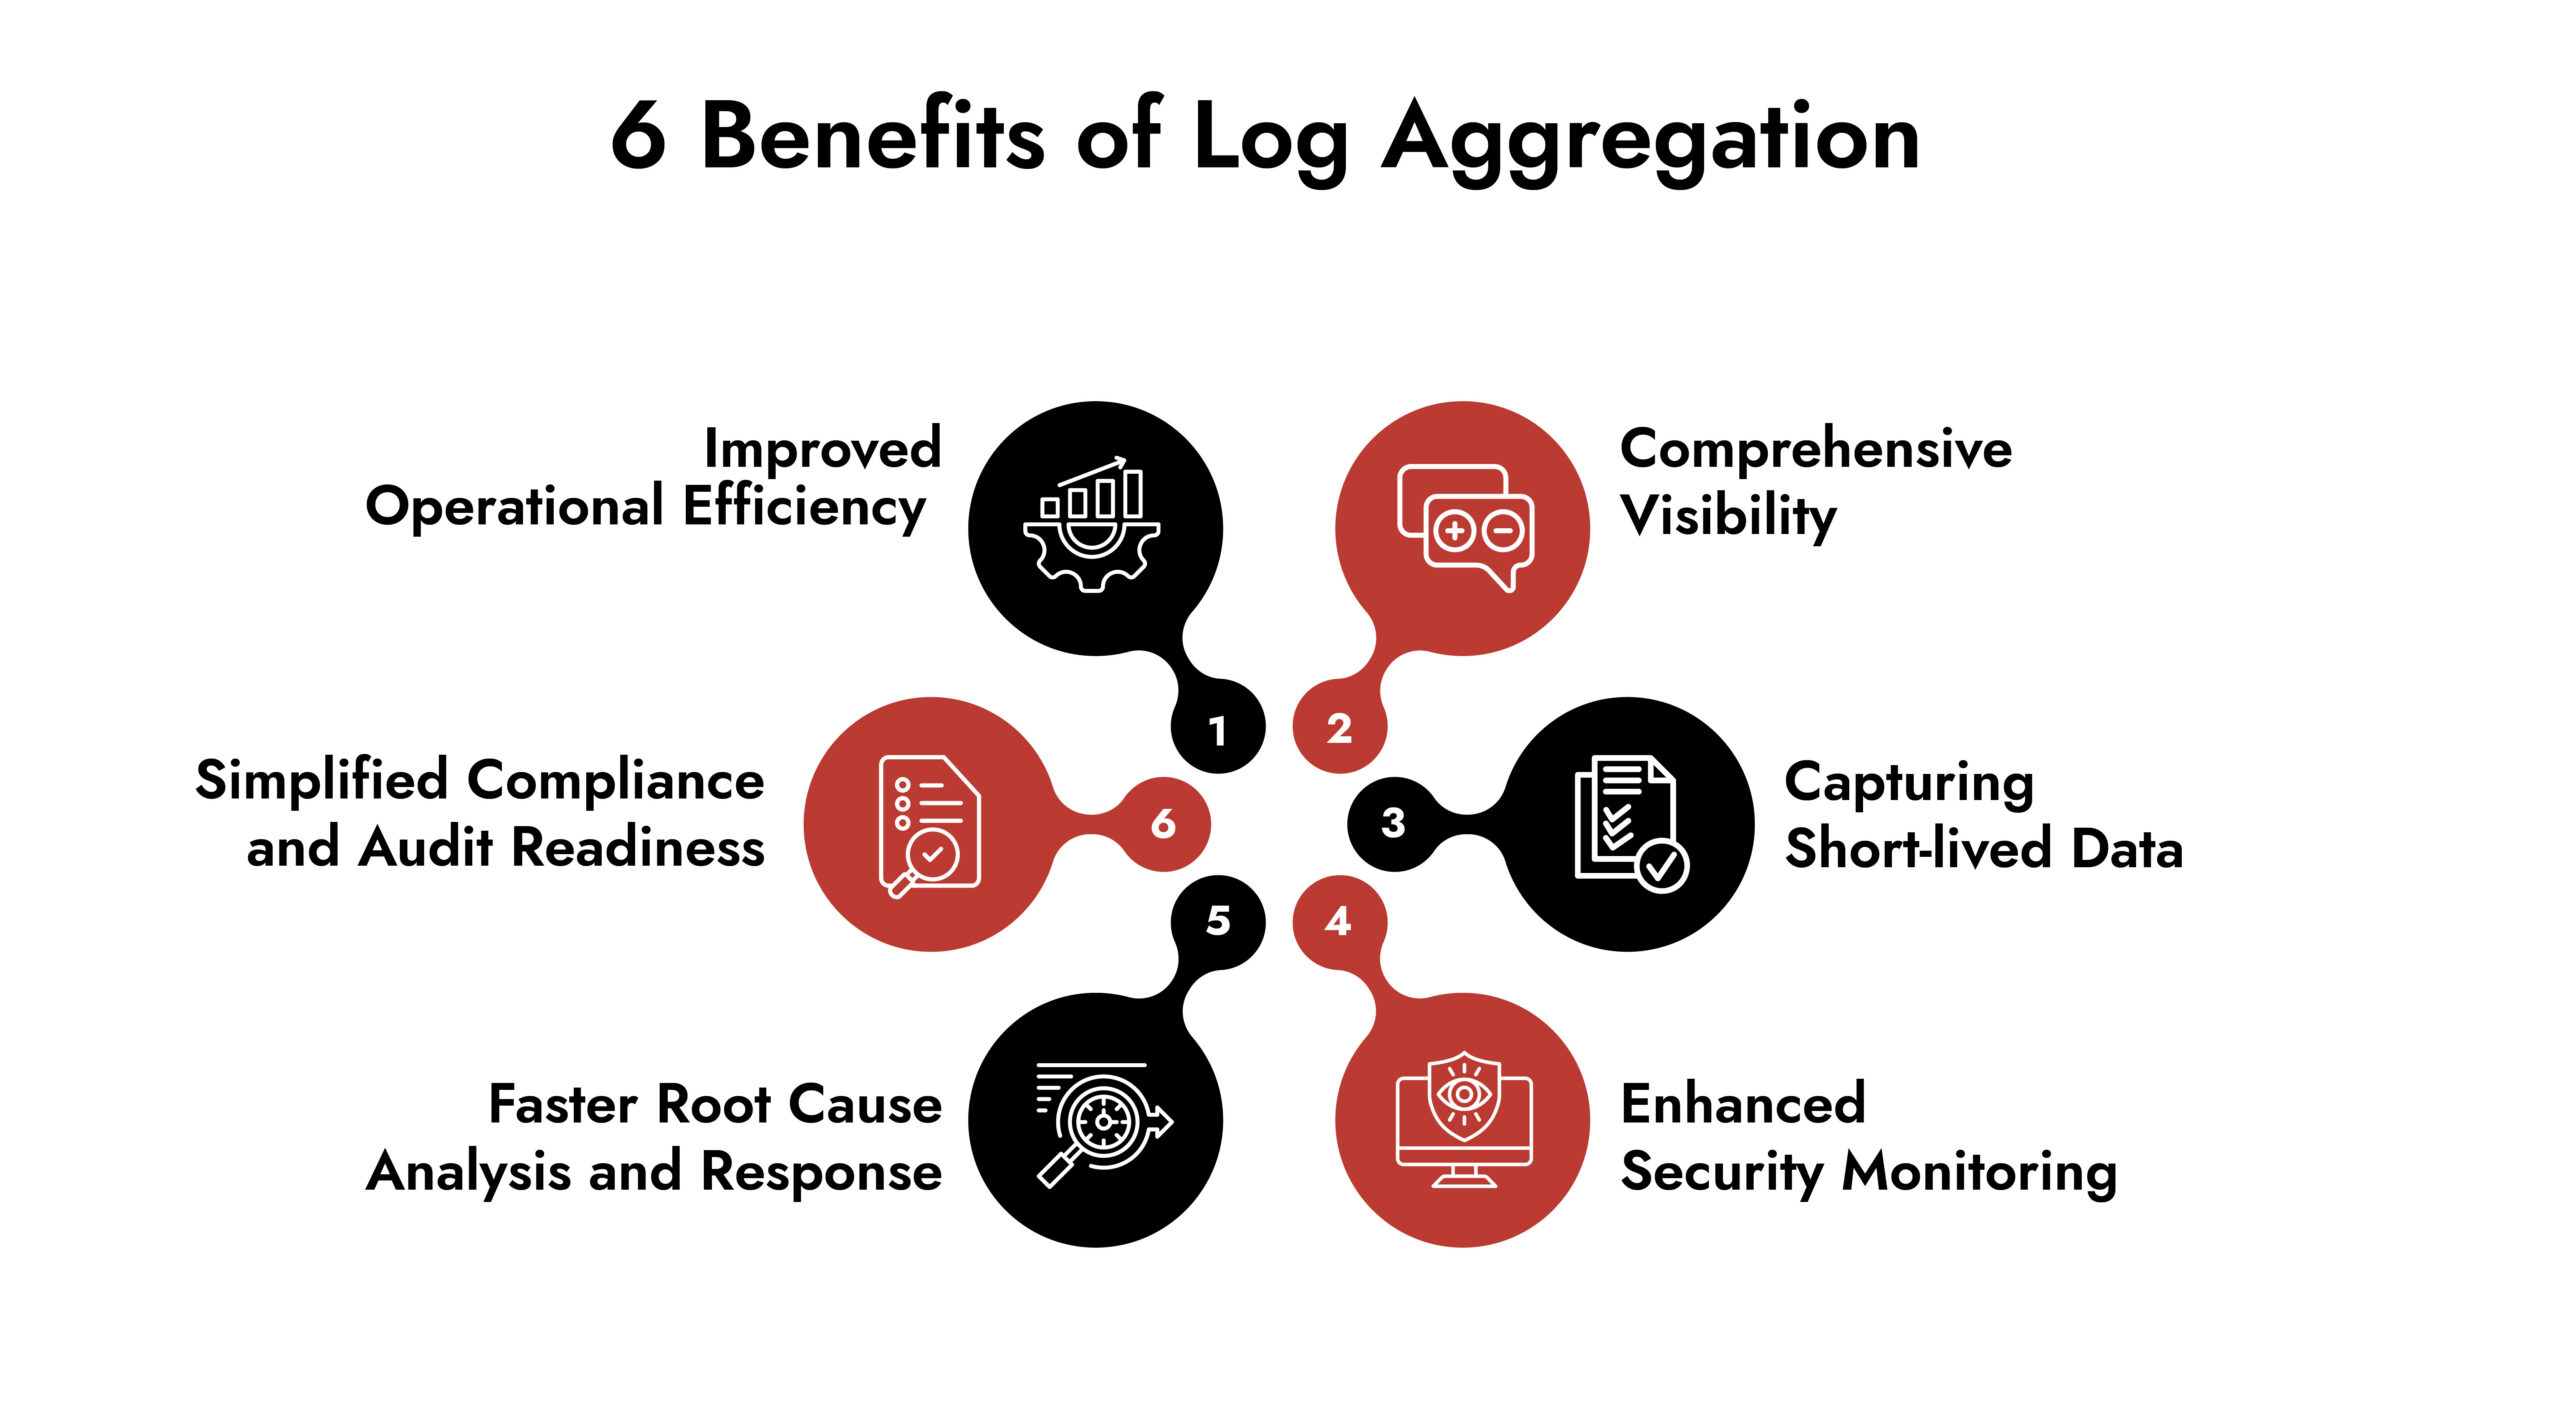
What are the Benefits of Log Aggregation?
Let us look at how log aggregation helps organizations in strengthening security and operations.
1. Comprehensive Visibility
When the data is scattered across the organization, connecting the dots for an insight seems like counting stars. Log aggregation overcomes this major obstacle by unifying the logs and giving 360-degree visibility across the IT infrastructure. Teams get access to a single source of truth in a centralized location as opposed to spending hours just collecting data.
This visibility helps the SOC teams accelerate their analysis and response. For CISOs, log file analysis gives insights into the risk posture for better strategic decisions around cybersecurity.
2. Capturing Short-lived Data
Modern cloud environments rely on containers, serverless functioning, and virtual workflows that exist for only a few seconds or minutes. Collecting and monitoring logs or data from such ephemeral resources manually is impossible. Advanced log aggregation solutions ensure that logs from such resources are collected before they disappear.
3. Enhanced Security Monitoring
Log aggregation is nothing but telemetry as far as security is concerned. The logs monitor and keep SOC analysts informed about unauthorized access attempts, suspicious behavior patterns, lateral movement indicators, and policy violations in real-time.
Log aggregation also ensures that the SOC team has consistent, complete, and recent data for analysis and detection.
4. Faster Root Cause Analysis and Response
During a security incident, every minute that is spent longer on analysis or any other procedure costs the organization. And unfortunately, the root cause does not exist in isolation; it may be due to a certain application logic or missed updates or external dependencies.
Log aggregation tools collects all the data and correlates them, largely simplifying analysis. This translates into faster root cause analysis and millions of savings.
For example, if your SOC detects unusual outbound traffic from a production server, with aggregated logs they can:
- Instantly search the related activities across the server
- Correlate with authentication logs to discover the user behind the activity
- Check application logs for unusual behavior
To execute all these activities manually, it would take hours, but with aggregated logs, this can be done within minutes.
5. Simplified Compliance and Audit Readiness
Regulatory guidelines demand comprehensive logging practices. GDPR requires data access audit logs, PCI DSS mandates cardholder data environment logs, SOC 2 requires monitoring and detection logs, and HIPAA demands audit controls for health information.
Log aggregation and management helps meet these requirements by applying consistent retention policies to produce audit-ready documents. It sets up the foundation for compliance by ensuring:
- Role-based access control to logs
- Audit trails of log access
- Protected log storage to ensure data integrity
- Automated compliance reporting
6. Improved Operational Efficiency
When the logs are available in a centralized location, cross-functional teams such as SOCs, IT operations, DevOps, and application teams can refer to an up-to-date single source of truth. This shared visibility eliminates conflicting interpretations and rework due to referencing outdated data.
This also means smoother handoffs, improved collaboration, and overall enhanced efficiency.
What Are Log Aggregation Tools?
Log aggregation tools collect logs from multiple sources and bring them into a central system where teams can store, search, and analyze the data.
Depending on the product, the platform may support sources such as:
- Servers and operating systems
- Applications and databases
- Firewalls and network devices
- Cloud infrastructure
- SaaS applications
- Endpoints
- Security products
- Containers and other dynamic workloads
The capabilities can vary considerably between tools. Some focus primarily on collecting and storing logs, while others add parsing, normalization, search, correlation, alerting, analytics, dashboards, or broader SIEM capabilities.
That distinction matters when comparing products. A platform that simply centralizes logs addresses a different requirement from one designed to turn those logs into security detections and investigation data.
What Should You Look for in a Log Aggregation Tool?
The right log aggregation tool depends on the size and complexity of the environment, the volume of data, retention requirements, and how the organization plans to use the logs.
Here are the capabilities worth evaluating:
Broad log source support – The tool should be able to collect logs from the technologies already deployed across the environment, including on-premises infrastructure, cloud services, SaaS applications, network devices, and security controls.
Reliable ingestion at scale – High-volume environments can generate large amounts of log data during normal operations, with sudden increases during incidents. The platform should be able to handle these volumes without creating significant gaps in collection.
Fast search and filtering – Centralizing logs has limited value if analysts still have to wait or sift through large amounts of irrelevant data. Search, filtering, and querying should make it practical to move from a broad event to the relevant records quickly.
Parsing and normalization – Different systems use different log formats. Parsing and normalization make those records easier to search and compare across sources.
Flexible retention and storage – Retention requirements differ by use case. Operational troubleshooting may require shorter retention, while investigations and regulatory requirements may call for longer periods. Storage options should accommodate those differences without making log management unnecessarily expensive.
Integration with security tools – Log aggregation often sits within a larger security environment. Integration with SIEM, threat intelligence, endpoint, network, and incident response technologies can help teams use aggregated data beyond basic troubleshooting.
Access controls and auditability – Logs can contain sensitive information. Look for role-based access controls, audit trails, and controls that help protect log integrity and restrict access appropriately.
Cloud and hybrid support – For organizations operating across data centers, cloud platforms, SaaS applications, and remote infrastructure, the tool should provide consistent visibility across those environments.
These capabilities also align with the evaluation criteria NetWitness currently highlights for log aggregation and log monitoring, including broad source support, scalable ingestion, search, retention, integration, and hybrid-environment support.
Log Aggregation Best Practices
Implementing a log aggregation platform does not automatically produce useful log data. The quality of the outcome depends on what gets collected, how it is managed, and how teams use it.
Define which logs matter – Start with the systems and events that are most relevant to security, operations, and compliance. Collecting everything without a clear purpose can increase storage requirements and make analysis harder.
Maintain consistent time synchronization – Accurate timestamps are essential when reconstructing a sequence of events. Systems should use synchronized clocks so events from different sources can be placed in the correct order.
Standardize log formats where possible – Consistent fields and formats make searching and analysis easier. Normalization becomes particularly important when logs from different vendors need to be compared.
Set retention policies by use case – Not every log needs to be stored for the same amount of time. Define retention periods based on regulatory requirements, investigation needs, operational value, and storage costs.
Protect access to logs – Restrict log access according to role and maintain records of administrative or investigative activity. Logs can contain usernames, IP addresses, system details, and other information that should not be broadly accessible.
Monitor collection health – A missing log source can create a blind spot. Regularly check whether expected sources are still sending data and investigate sudden changes in log volume or ingestion.
Reduce unnecessary noise – Not every event deserves equal attention. Filtering duplicate, irrelevant, or excessively verbose data can help analysts work with a more manageable dataset while preserving information that may be important for investigations.
Review coverage as the environment changes – New cloud services, applications, devices, and security controls introduce new sources of telemetry. Log coverage should therefore be reviewed whenever the environment changes, rather than treated as a one-time configuration exercise.
How can NetWitness Help?
In the ever-changing threat landscape, log aggregation is definitely crucial to fortify cybersecurity defense. But it is just the first layer. Organizations should go an extra mile and employ solutions that collect data, analyze it to detect threats and as well as generate alerts to support incident response.
NetWitness SIEM captures logs from 350+ sources, including AWS, Azure, Salesforce, etc., using Syslog, ODBC, SFTP, FTPS, and SNMP protocols.
It goes beyond log aggregation and manages alerts as well as generates reports using templates that comply with regulatory standards such as SOX, HIPAA, PCI, and NERC.
Key features of NetWitness SIEM include:
- Centralized Log Management
- Dynamic Parsing & Metadata
- Cloud-Ready Deployment
- Customizable Reporting
- Automated Log Source Directory